Are you concerned about how QR code payments impact your PCI DSS compliance? Handling customer transactions through visual codes introduces specific security risks that can lead to steep non-compliance penalties or data breaches if not managed properly. This guide explains how to implement secure QR workflows that satisfy compliance standards and protect cardholder data.
Understanding QR Codes and PCI DSS Requirements
The Payment Card Industry Data Security Standard (PCI DSS) applies to any entity that stores, processes, or transmits cardholder data, or impacts the security of the cardholder data environment. A QR code itself functions as an entry or redirection mechanism rather than an isolated payment system. Because of this, your compliance obligations depend entirely on how customer data flows through your technical environment after a scan.
When evaluating QR kodovi za plaćanja, merchants typically encounter two main transaction flows:
- Merchant-presented mode: You display a static or dynamic code on a screen, invoice, or printed stand that the customer scans using their smartphone camera or a payment application.
- Consumer-presented mode: The customer displays a code generated by their mobile banking app or digital wallet, which your point-of-sale scanner reads to complete the transaction.
In consumer-presented flows, the customer app generally supplies a single-use payment token, keeping raw primary account numbers away from your local systems. Merchant-presented flows require careful network design because the scanned link directs the customer device to a payment interface. If your systems generate the code, host the landing page, or handle the resulting transaction data, those systems fall directly into your compliance scope.
Assessing Security Risks in QR Payment Workflows
Before establishing compliance controls, you must identify where vulnerabilities arise during the payment interaction. Standard card terminals use hardware encryption modules, whereas visual codes rely on mobile browsers and physical displays that attackers can manipulate.
Physical tampering remains one of the most widespread threats. Fraudsters execute quishing attacks by placing counterfeit adhesive labels over legitimate payment codes in public locations such as parking meters, restaurants, and retail checkout counters. When an unsuspecting buyer scans the overlay, the code directs them to a spoofed payment gateway configured to harvest card numbers and sensitive authentication data.
Digital vulnerabilities present equal operational risks. Unencrypted payment links leave transactions exposed to man-in-the-middle attacks across public Wi-Fi networks. Furthermore, malicious redirects can trigger drive-by downloads that compromise consumer devices. Reviewing how to mitigate QR code payment risks helps your organization establish defenses against counterfeit domains and fraudulent payment capture. Knowing how to train your staff to spot fake QR codes helps prevent deceptive physical overlays from remaining unnoticed.
Scoping Architectures and SAQ Eligibility
Your technical payment architecture dictates your audit workload and determines which Self-Assessment Questionnaire (SAQ) applies to your organization. Outsourcing payment processing to a third party does not eliminate your compliance obligations, but selecting the right integration model significantly limits your exposure.
| Architecture Type | Data Flow Description | Primary PCI Impact | Applicable Validation |
|---|---|---|---|
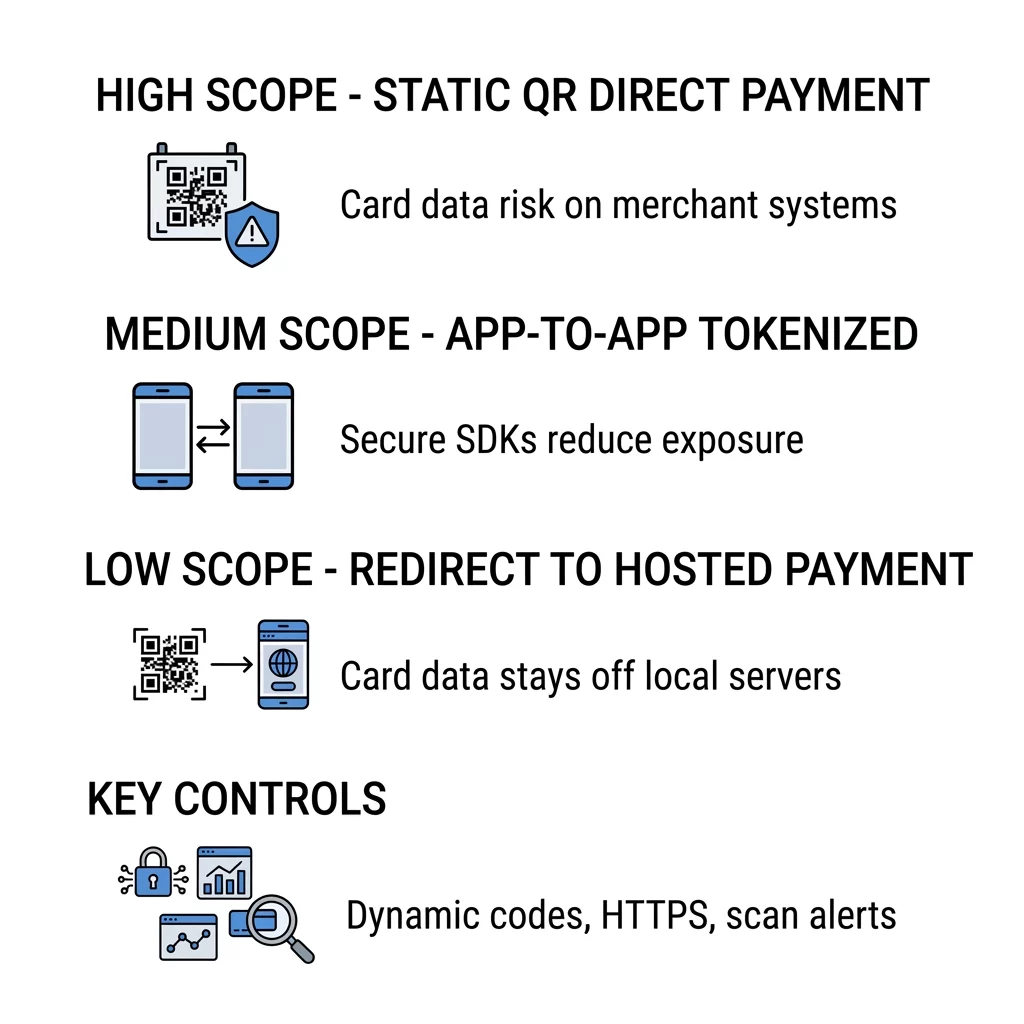
| Hosted URL Redirect | Scanned code sends mobile browser directly to an external payment processor | Merchant network never touches or stores cardholder data | SAQ A |
| Embedded Merchant Page | Scanned code loads merchant page containing an embedded third-party iframe | Merchant site affects the security of the payment environment | SAQ A or SAQ A-EP |
| Direct API Integration | Merchant application captures card details directly from the user and transmits via API | Merchant infrastructure actively processes sensitive cardholder data | SAQ D |
A URL redirect architecture offers the most direct path to scope reduction. Under this model, the QR code transfers the customer directly to a checkout page hosted entirely by an accredited payment service provider. Because your servers never store, process, or transmit payment account data, you typically qualify for SAQ A validation.
If your website controls any scripts or stylistic elements on the checkout page, you may be required to validate under SAQ A-EP. Under PCI DSS v4.0.1, requirements 6.4.3 and 11.6.1 mandate strict script management and tamper-detection mechanisms for all scripts executing in the consumer’s browser on payment pages. Managing these requirements demands continuous script inventories, written business justifications, and active integrity monitoring.
Obezbedite svoj tok plaćanja Need to create trackable, branded payment touchpoints that route customers safely to your payment gateway? Use the dinamički generator QR kodova to maintain total control over destination URLs and track scan activity in real time.
Technical Best Practices for Payment Security
Maintaining an auditable payment flow requires pairing strong data protection standards with active system oversight. Implementing controls that align with modern security baselines ensures transaction integrity from scan to settlement.
- Deploy dynamic codes instead of static links: Dynamic codes point to a central management server that routes the customer to the final payment destination. If an issue occurs, you can change the target URL or deactivate the link instantly without replacing printed materials.
- Enforce end-to-end encryption: Ensure that all payment redirects utilize HTTPS with valid TLS certificates issued by recognized authorities. Unencrypted HTTP transmissions violate PCI DSS requirement 4.1 and leave cardholder data exposed to interception.
- Incorporate transaction-specific parameters: When possible, generate dynamic codes tied to an exact order amount, invoice number, and short expiration window. This prevents replay attacks where malicious parties attempt to reuse stale payment references.
- Standardize EMVCo specifications: Adopting recognized standards for visual payment codes ensures consistent data payload structures, reliable error correction, and uniform processing across diverse financial platforms.
- Monitor scan telemetry for anomalies: Track scan volumes, device headers, and geographic origins. A sudden burst of scans from unfamiliar locations or uncharacteristic IP subnets often signals an ongoing quishing campaign or automated probe.
Razumevanje najbolje prakse za bezbednost QR kodova u sajber odbrani allows you to implement layered protections such as tokenization, multi-factor administrative access, and real-time endpoint telemetry. Pairing these safeguards with QR code payment security and speed gives your customers a fast checkout while preserving strict data boundaries.
For merchants who use payment gateways like PayPal, using a dedicated PayPal generator QR kodova simplifies setting up direct-to-checkout flows that keep primary account numbers away from your internal network.
Operational Controls and Physical Tamper Prevention
Physical security controls are just as critical as digital network defenses. Point-of-sale areas with high customer foot traffic require ongoing oversight to prevent criminal interference.
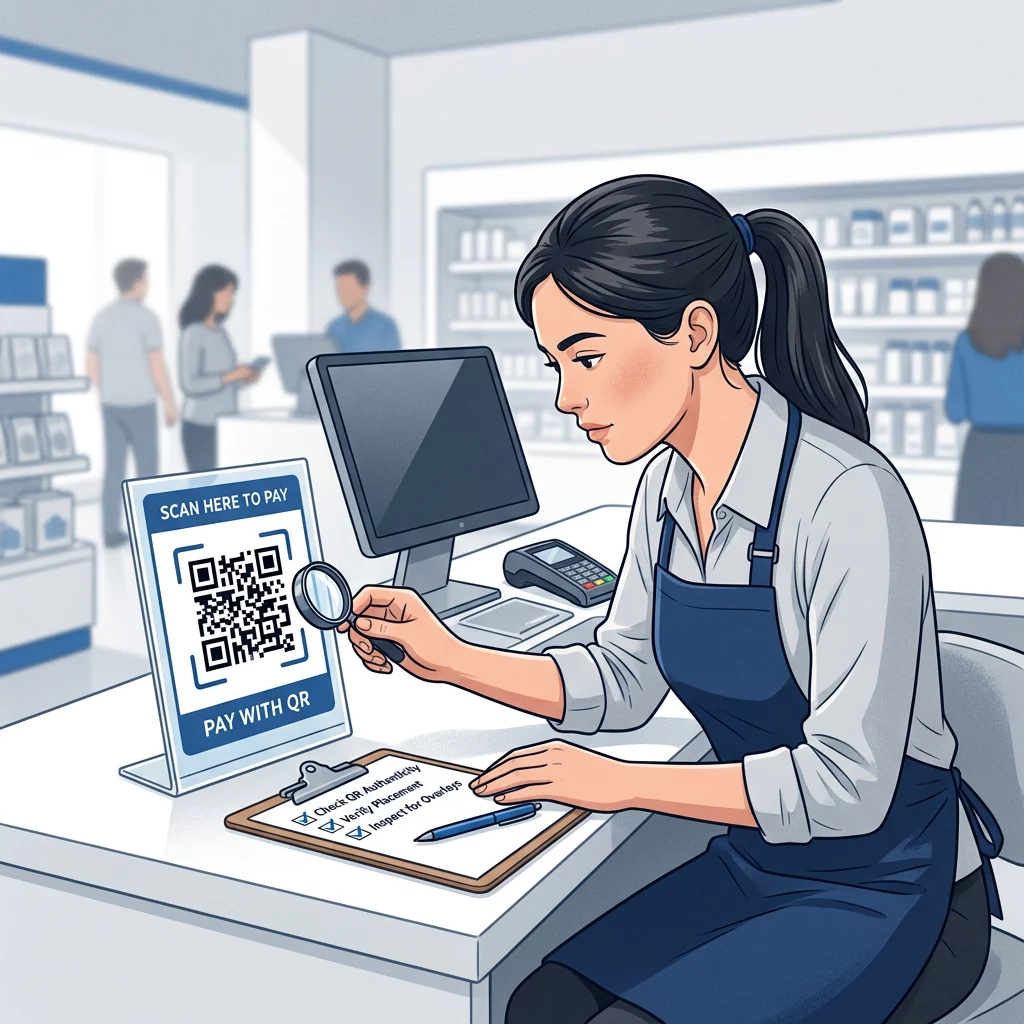
Establish a daily inspection routine where staff physically examine every displayed code before opening and after closing. Employees should look for peeling edges, misaligned stickers, variations in print surface texture, or duplicate signage. If an employee discovers signs of tampering, your documented incident response procedures must instruct them to take the code out of service immediately and notify management.
Merchants must also respect regional consumer data protections alongside financial compliance. Reviewing key QR code privacy laws ensures your customer tracking and marketing analytics do not run afoul of statutory requirements like GDPR or CCPA while gathering scan data.
Completing Your Compliance Validation
Validating your compliance status requires formal coordination with your acquiring bank or payment brand. While the PCI Security Standards Council defines technical benchmarks, individual payment brands and merchant acquirers determine your specific validation tier, reporting deadlines, and assessment forms.
Review your processing agreements to confirm your merchant level and request your reporting requirements directly from your acquiring processor. If your infrastructure includes external-facing web applications or public IP addresses that interact with payment channels, arrange for regular vulnerability scans conducted by an Approved Scanning Vendor (ASV). Complete your designated SAQ along with an official Attestation of Compliance (AOC), submit the documentation to your processing partner, and schedule an annual review to maintain ongoing operational compliance.
Često postavljana pitanja
No. While routing customers to a hosted payment portal reduces your compliance burden to an assessment like SAQ A, you remain responsible for validating your setup annually, monitoring service providers, and safeguarding your physical and digital touchpoints.
Dynamic QR codes route user requests through a centralized management server, allowing you to log scan timestamps, IP addresses, user agents, and redirection targets, which provides the detailed audit trail required to investigate suspicious activity.
Remove the compromised display from customer access immediately, notify your payment processor and internal security team, activate your incident response protocol, and inspect all nearby checkout displays for similar unauthorized modifications.