Maakt u zich zorgen dat het bijhouden van uw QR-codescans kan leiden tot hoge AVG-boetes? Het overtreden van privacyregelgeving kan de reputatie van uw merk schaden en leiden tot juridische sancties die de voordelen van gegevensverzameling ruimschoots overtreffen. Deze gids legt uit hoe u bruikbare inzichten kunt verzamelen met behulp van anonimisering en transparante verwerking om volledig compliant te blijven.
Het begrijpen van het gegevensverzamelingsproces
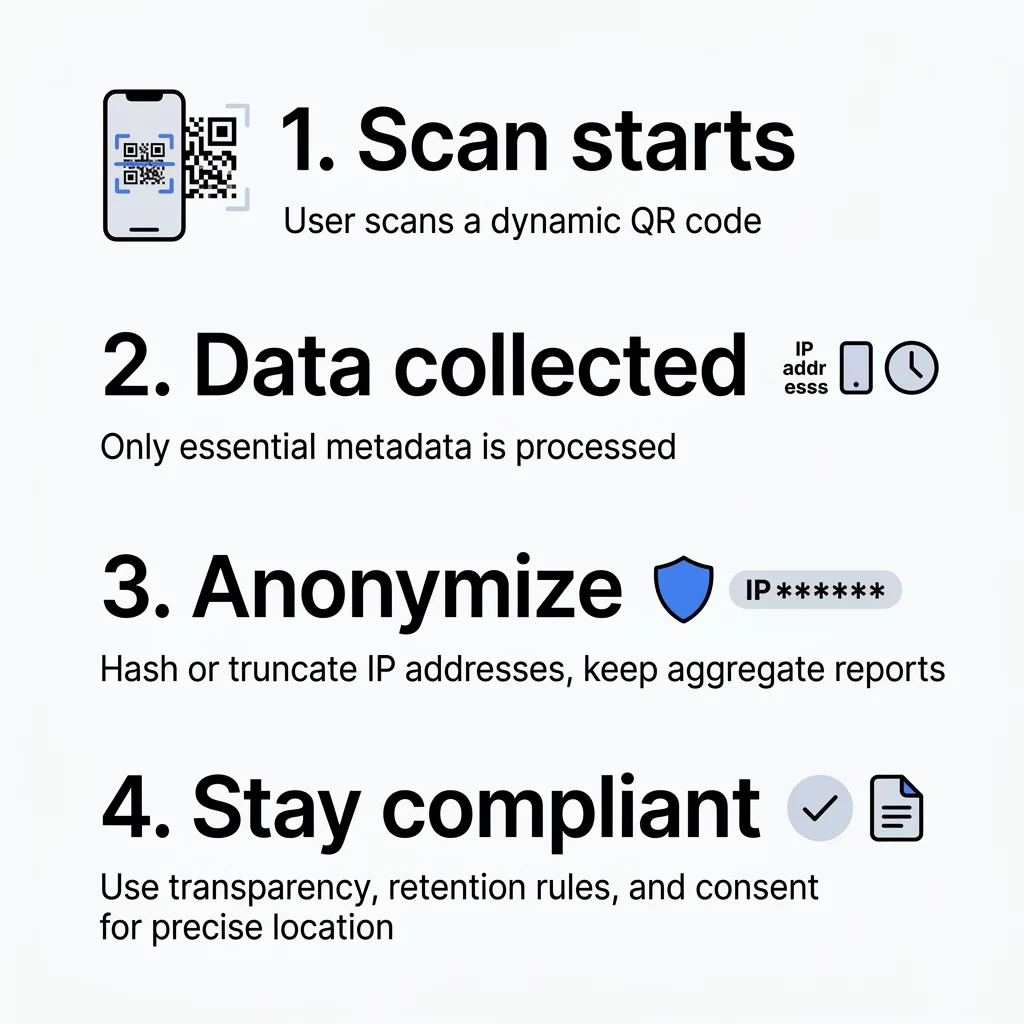
To track performance, businesses typically use dynamic codes that pass through a tracking server before reaching their final destination. Think of this server as a high-speed digital checkpoint that logs technical metadata about the interaction before completing the redirect. While this redirection enables ongoing measurement and editable links, it means your system processes technical data points subject to European privacy rules.
Dynamic scan tracking typically captures several categories of information during an interaction:
- Internet Protocol (IP) addresses used to estimate general geographic location
- Device attributes such as operating system version, device model, and browser type
- Exact timestamps detailing the date, hour, and minute of each scan event
- Campaign markers such as UTM parameters attached to the destination URL to identify physical placements
Begrijpen welke gegevens dynamische QR-codes verzamelen helps you distinguish between harmless interaction metrics and technical records that fall under regulatory oversight.
Wanneer scangegevens persoonlijke informatie worden
Under Article 4(1) of the General Data Protection Regulation (GDPR), personal data encompasses any information relating to an identified or identifiable natural person. The European Court of Justice confirmed that dynamic IP addresses constitute personal data because online identifiers can be linked back to individual users when combined with additional records held by internet service providers.
The architecture of your QR code dictates whether personal data processing occurs:
- Static QR codes embed destination data directly into the black-and-white matrix pattern. They do not route through intermediary redirect servers and collect zero personal data from users.
- Dynamic QR codes route scanners through a management server to log performance before forwarding the user. This routing enables campaign editing, but it exposes the server to user IP addresses and device information.
To minimize exposure from the outset, you can design QR codes with minimal data collection by collecting only the high-level engagement figures needed for marketing decisions.
Strategieën voor gegevensanonimisering
The most effective way to eliminate GDPR liability in analytics is to make the data truly anonymous. According to GDPR Recital 26, principles of data protection do not apply to anonymous information that cannot be linked to an identifiable person. If an individual is no longer identifiable through singling out, linkability, or inference, the data falls entirely outside the regulation.
To achieve valid anonymization, apply privacy techniques at the ingestion point:
- Truncate IP addresses immediately upon receipt by stripping the final octets before writing records to persistent storage.
- Replace direct identifiers with one-way cryptographic hashes combined with salt strings that change regularly.
- Aggregate interaction counts into broad metrics such as total daily scans per city rather than maintaining individual user event logs.
- Enforce automated deletion schedules so raw server connection logs are purged as soon as the redirect completes.
Reviewing technical anonymization methods for QR code data allows you to choose methods like masking or perturbation that preserve reporting utility while eliminating individual identity.
Organizations frequently confuse pseudonymization with true anonymization. Pseudonymization replaces direct identifiers with artificial keys or random tokens, but because the records can still be re-identified using supplementary keys, pseudonymous records remain personal data under EU law. Establishing clear data retention rules for QR code analytics ensures that any temporary identifiers used during redirect routing are permanently deleted.
Track Campaign Performance with Built-In Privacy Controls Need actionable scan insights without violating European privacy standards? Use the QR code analytics platform to monitor campaign engagement through aggregated, privacy-conscious reporting.
Een rechtmatige grondslag kiezen voor verwerking
Before collecting personal identifiers, Article 6 of the GDPR requires you to establish a lawful basis for processing. When measuring QR interactions, organizations primarily rely on two distinct legal grounds:
- Legitimate Interests: Businesses can often justify basic aggregated reporting, such as counting scans or identifying device operating systems, under Article 6(1)(f). You must conduct a Legitimate Interests Assessment (LIA) to demonstrate that your business purpose does not override the fundamental rights and expectations of the user.
- Consent: Explicit consent under Article 6(1)(a) is mandatory whenever you access hardware-level device features or collect precise GPS coordinates. Valid consent must be freely given, specific, informed, unambiguous, and documented through an active affirmative action before data capture begins.
Cookie rules also apply under the ePrivacy Directive. If your tracking redirect sets tracking cookies or reads stored identifiers from the user’s mobile browser, you must present a consent prompt before setting those tracers unless an exemption applies.
Best Practices for Privacy by Design
Maintaining compliance is an ongoing operational commitment that requires a privacy-by-design architecture. Rather than treating compliance as a legal patch applied after launch, privacy safeguards should be built directly into your physical marketing collateral and digital routing infrastructure.
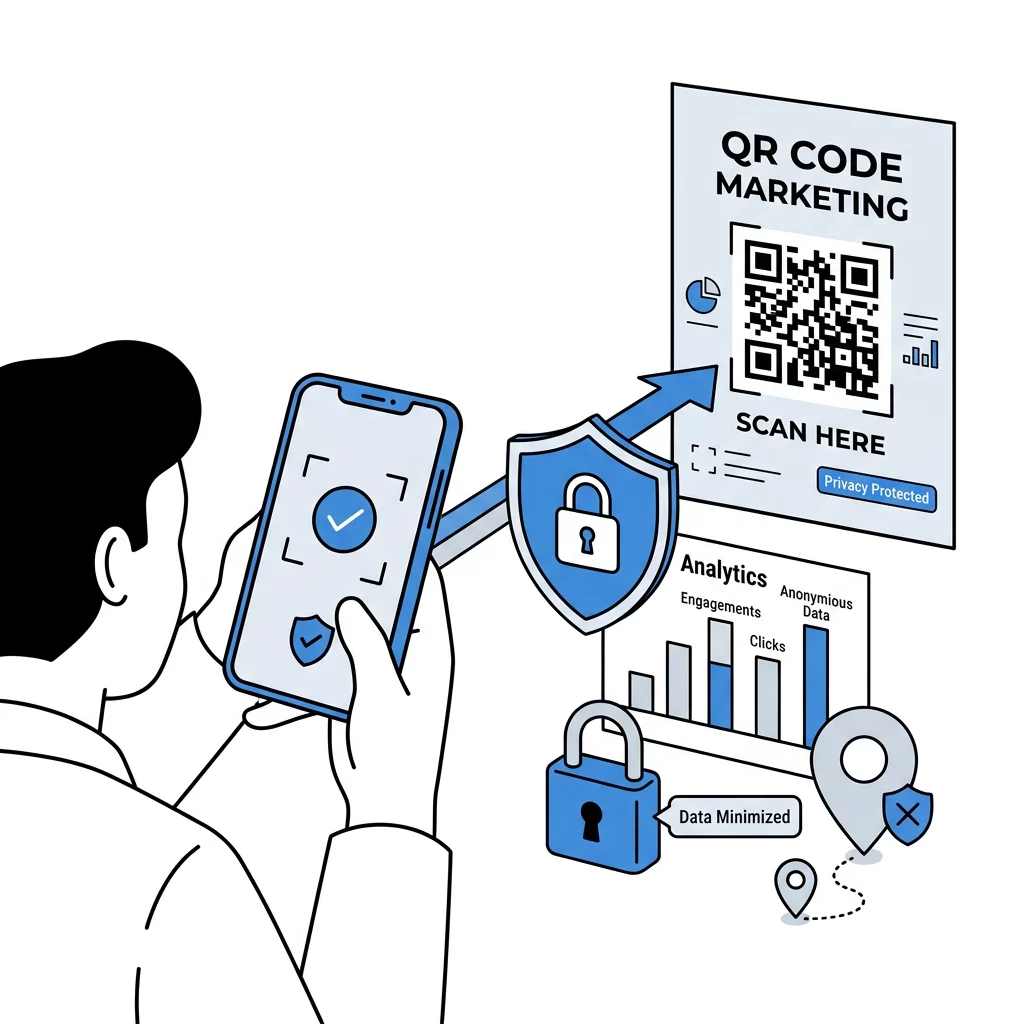
To safeguard user rights and streamline your marketing workflows, apply these practical rules:
- Practice strict data minimization by relying on non-precise, city-level geographic data rather than tracking exact GPS coordinates.
- Display concise privacy notices near the printed code so users understand what occurs when they point their smartphone camera.
- Consult an overview of QR code privacy laws to verify compliance across cross-border campaigns subject to international data privacy statutes.
- Review platform settings in your dynamische QR-codegenerator to ensure default configurations strip identifying IP octets automatically.
- Restrict data sharing arrangements with downstream marketing networks and ensure data processor agreements are executed with software vendors.
Exploring comprehensive QR-codefuncties gives marketing teams the ability to customize user journeys, manage code redirections, and maintain data controls from a single management platform.
Veelgestelde vragen
A cookie banner is required only if your tracking redirect or landing page places non-essential cookies or tracking scripts on the user’s device. If your QR code uses cookieless server-side analytics with anonymized IP addresses, a cookie banner is generally not needed for the scan itself.
Tracking approximate geographic location derived from an anonymized IP address is legal under legitimate interests because it does not identify the individual. Tracking precise location using device-level GPS sensors is considered sensitive personal data and requires explicit, prior consent.
Anonymized scan data cannot be linked back to an individual natural person and is completely exempt from GDPR requirements. Pseudonymized scan data replaces personal identifiers with unique codes or keys, but remains subject to GDPR rules because re-identification remains technically possible.
Maintaining Compliance While Measuring Results
Measuring real-world campaign engagement does not require sacrificing individual user privacy or risking regulatory penalties. By implementing IP anonymization at ingestion, choosing the proper legal basis for tracking, and applying strict data minimization, your team can capture actionable performance data while remaining fully compliant with EU regulations.
Audit your current scan tracking workflows, eliminate unnecessary device tracking, and transition your active marketing materials to privacy-focused dynamic QR tracking today.